It Started With a Phone Call
We tend to imagine a cloud attack as something complicated:
Breaking into a server, exploiting a critical vulnerability, or at least running a line of code that looks impressive in an incident report.
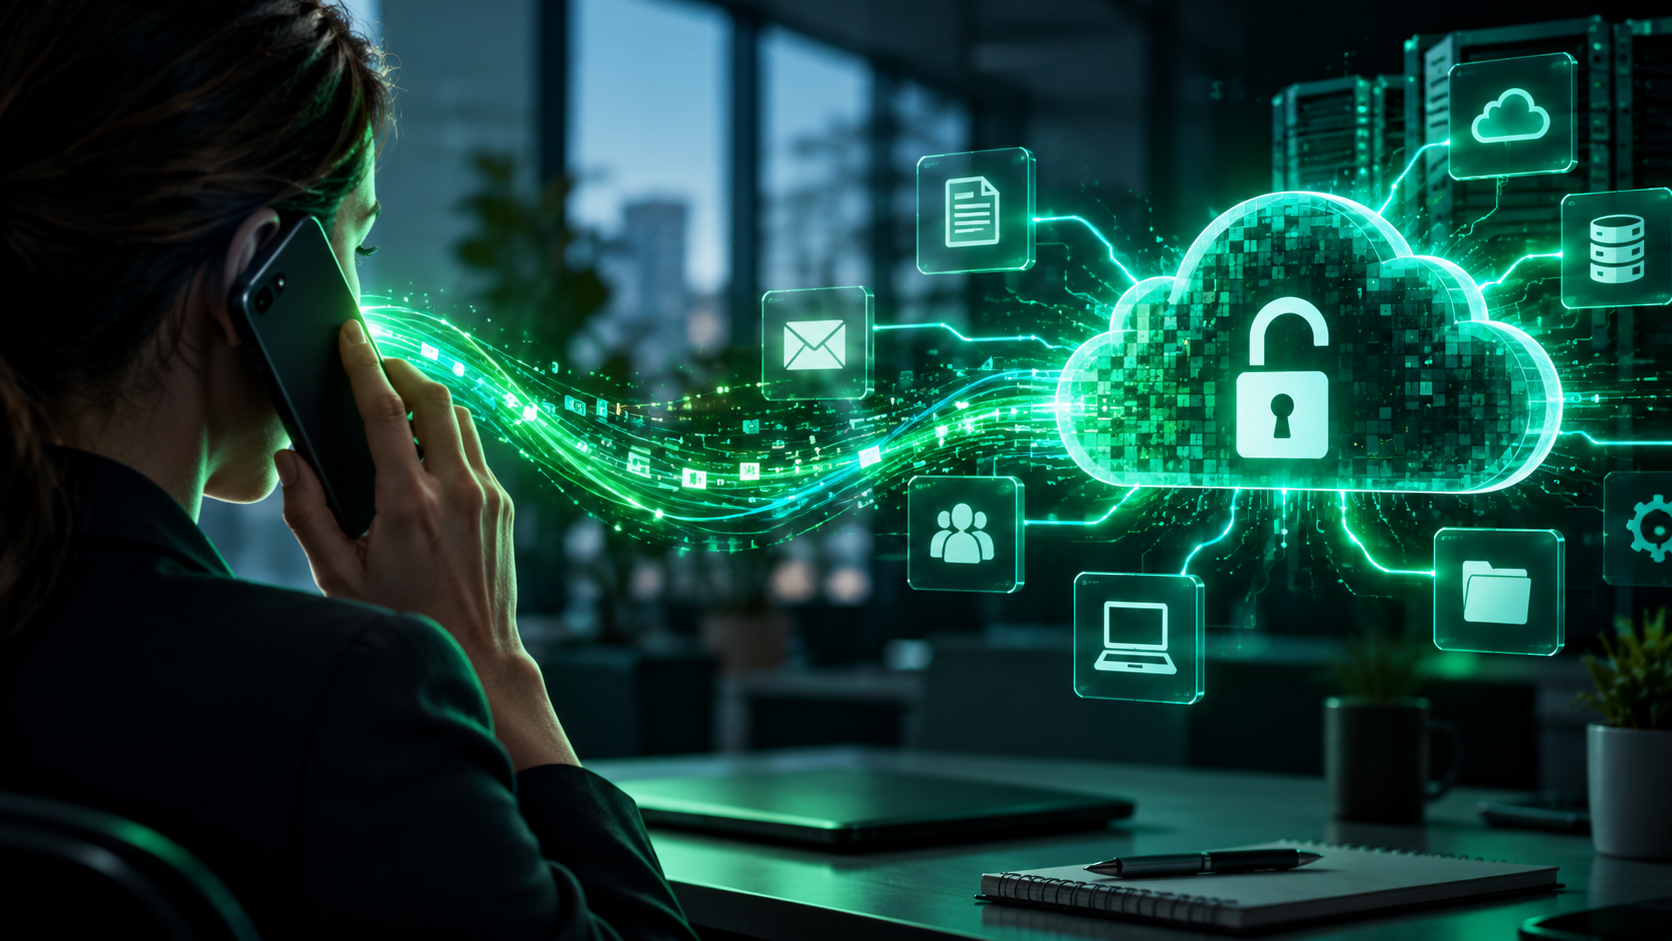
But in the BlackFile campaign, the attackers started with something much simpler: a phone call to an employee.
In May 2026, Google Threat Intelligence Group published details about an extortion campaign carried out by UNC6671 under the name BlackFile. The group targeted dozens of organizations across North America, the UK, and Australia.
Its main targets were Microsoft 365 and Okta environments.
No Vulnerability Required
The interesting part is that the attackers did not exploit a vulnerability in any cloud service.
They simply called employees, pretended to be members of the IT team, and claimed that an MFA (Multi-Factor Authentication) update or migration to a new passkey was required.
To make the story more believable, the attackers sometimes called the employee’s personal phone. This allowed them to bypass corporate security controls and move the conversation away from official support channels.
Stealing Access in Real Time
The employee was then directed to a fake login page designed specifically for the organization, which looked like the real SSO portal.
When the victim entered their username, password, and verification code, the attackers forwarded those details to the legitimate service in real time.
Immediately after signing in, they registered a new MFA device under their control.
In other words, the employee thought they were updating their authentication settings, but they were actually adding the attacker to the list of approved devices.
One Account, Multiple Cloud Services
From that point, the attackers did not need to compromise every system separately.
They used the SSO session to move between SharePoint, OneDrive, and other SaaS platforms, including Salesforce and Zendesk, depending on the permissions of the compromised account.
Searching for the Most Valuable Data
During the attacks, they searched for documents containing terms such as:
- Confidential
- SSN
- Internal
- Proposal
- VPN
Apparently, the attackers also understood that there was no reason to read every folder when they could simply ask the search function to show them the information the organization least wanted them to find.
When “File Access” Becomes Data Theft
After locating valuable data, they used PowerShell, Python, and legitimate APIs to extract large amounts of files from SharePoint and OneDrive.
In some cases, the activity was recorded as FileAccessed rather than FileDownloaded.
From the monitoring system’s point of view, the user had “only accessed” the file – while its contents were already being sent directly to attacker-controlled infrastructure.
From Data Theft to Extortion
After the data theft came the extortion.
Victims received payment demands with short deadlines ranging from 24 to 72 hours. In some incidents, the attackers also harassed employees and launched DDoS attacks to increase the pressure.
The Attack Chain
The attack chain looked like this:
Phone call → Theft of SSO and MFA details → Registration of a new device → Movement across cloud services → Data theft → Extortion
In other words, the attackers did not break into the cloud.
They logged in using a valid account, the correct password, approved MFA, and permissions that the organization had already granted.
How Can Organizations Protect Themselves?
- Move to phishing-resistant MFA, such as FIDO2 or passkeys.
- Require strong identity verification before password resets or MFA changes.
- Alert on the registration of new authentication devices, especially following a help desk call.
- Restrict cloud access to managed and compliant corporate devices.
- Monitor large-scale file access, not only download events.
- Detect unusual use of PowerShell, Python, and APIs against SaaS platforms.
- Revoke active sessions and tokens when account compromise is suspected.
What Can Individuals Do?
Never share an MFA code or approve a login request because of a phone call. If an IT representative asks you to make changes to your account, end the call and contact the help desk directly through an official channel.
It is important to remember that MFA is a valuable security layer, but it is not magic.
If the user approves the attacker, everything may look completely legitimate to the cloud platform.
Sometimes there is no malware, no exploit, and no compromised server.
There is only one legitimate identity that someone else has started using.
Source: [Google Threat Intelligence Group – Inside a BlackFile Vishing Extortion Operation](https://cloud.google.com/blog/topics/threat-intelligence/blackfile-vishing-extortion-operation/


